Delphos Labs Blog


Threat Intel: Alinubx.sys. The Renamed CcProtect Driver Behind a 40-Brand Malware-as-a-Service Campaign
Alinubx.sys is a renamed CcProtect driver, Microsoft-attested, that terminated 145 AV and EDR processes in the fake LastPass Authenticator campaign Delphos analyzed.


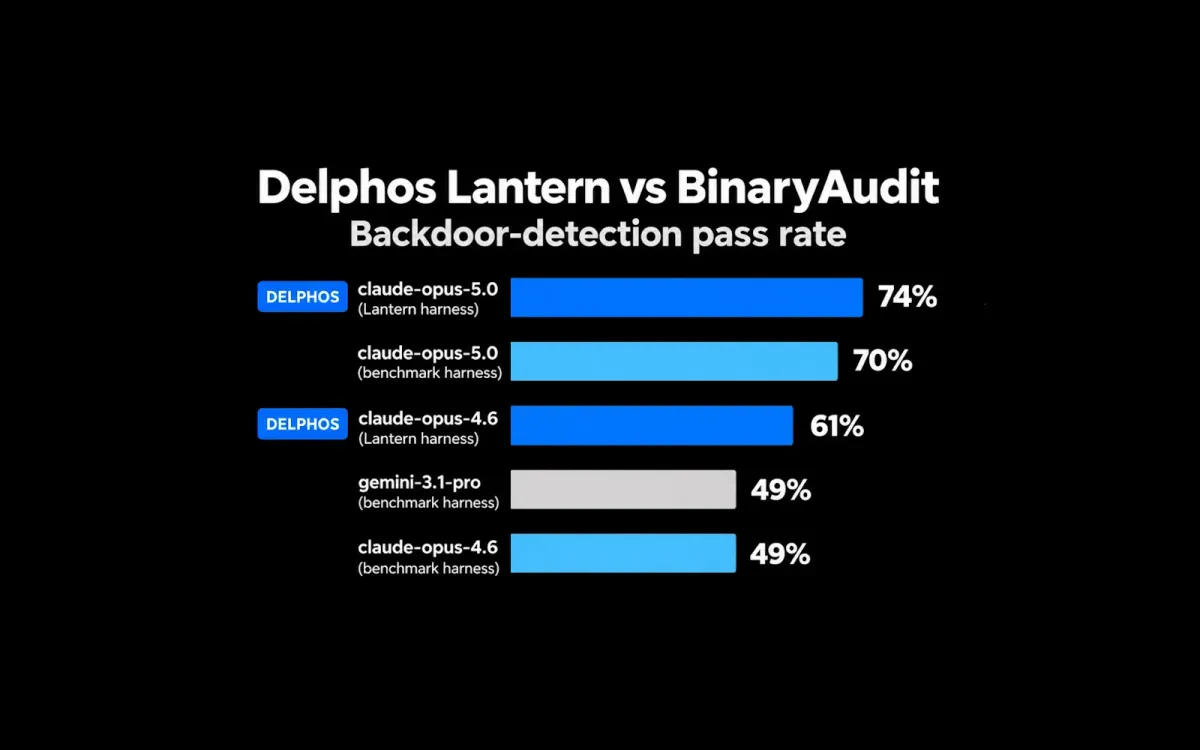
Delphos Lantern scores #1 on BinaryAudit backdoor detection: by mean, peak, floor, and reproducibility
Delphos Lantern’s harness with Opus 5.0 outperforms every published configuration on Quesma's independent BinaryAudit backdoor-detection benchmark.

Delphos outscores commercial decompilers on DecBench
Delphos Lantern takes first place on the overall metric and first place on elusive types metric


The USB Camera That Freezes Windows: A usbvideo.sys Descriptor Parser DoS Microsoft Won't Fix
A usbvideo.sys descriptor-parser DoS: a USB Video device with bLength=0 can pin kernel CPU and block USB enumeration. MSRC closed it without a fix.

CVE-2026-50321. How A Normal WinUSB Feature Exposed A Pipe-Lifetime Race
CVE-2026-50321: an unsynchronized free-then-null window in winusb.sys leaves a pipe-context pointer dangling for other contexts to use — reliably a BSOD, potentially an EoP.

Delphos Labs Selected by AFWERX for SBIR Phase I to Advance AI-Powered Analysis of Software Artifacts
Delphos Labs selected by AFWERX for an SBIR Phase I to advance AI-powered analysis of source-denied software for Air Force cybersecurity and assurance.


Threat Intel: ValleyRAT. A Zero-Detection Stager Classified 24 Hours Before Its First Signature
A Chinese-language ValleyRAT stager, zero AV detections, pulling a second-stage payload from AWS S3, classified in 5 minutes, 24 hours before first signature.

Threat Intel: libpsl-5.dll. A Sideloading DLL Padded to 55MB, Undetected by 60+ AV Engines for Six Days
The real payload is 3.3MB. The other 52MB is junk padding, appended to slip past scanners. Its code overlaps several known info-stealer families.

fast16: From Stripped Binary to Sabotage Finding in Minutes
The Delphos Labs agent analyzed fast16, a 2005 nation-state sabotage framework, starting from two stripped binaries and no context.

DirtyCBC: When Linux Kernel Decrypt-Before-MAC Turns Authenticated Encryption Into a Page-Cache Write
Linux kernel page-cache poisoning via AES-256 chosen-plaintext on the RxGK RESPONSE path and why authenticated encryption did not stop it.

Introducing Delphos Labs: Securing the Software That Actually Runs
Revealing hidden threats in compiled software without source code.